
Intuitus
Briefings
Weekly threat intelligence from the Intuitus analyst team — what changed, who it affects, and what to do about it.
-
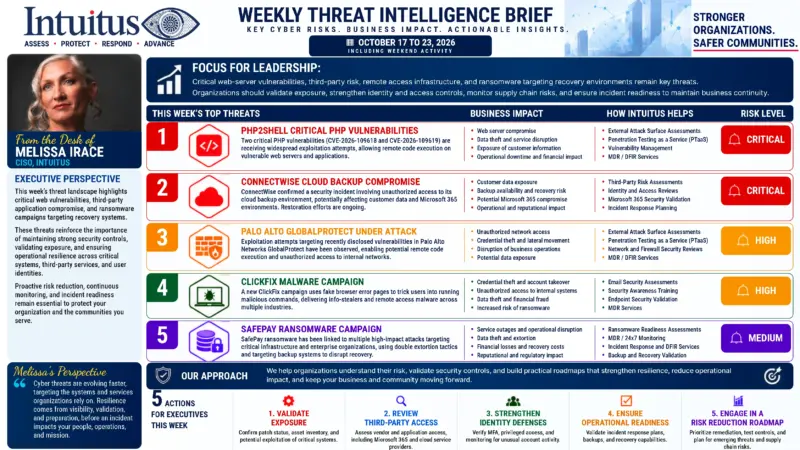
Weekly Threat Intelligence Brief, 17 to 23 October 2026
Critical web-server flaws, third-party risk and ransomware aimed at recovery lead the week: PHP2Shell, the ConnectWise cloud backup compromise, Palo Alto GlobalProtect, ClickFix and SafePay.
-
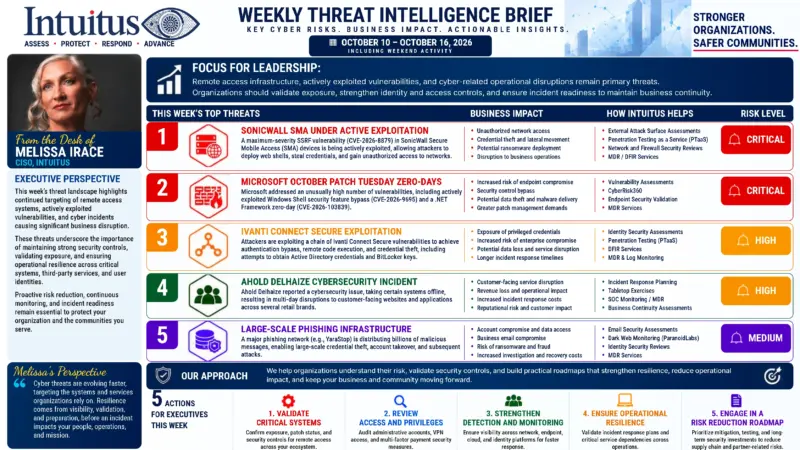
Weekly Threat Intelligence Brief, 10 to 16 October 2026
Remote access systems, actively exploited vulnerabilities and disruptive incidents lead the week: SonicWall SMA, October Patch Tuesday zero-days, Ivanti Connect Secure, Ahold Delhaize and mass phishing.
-
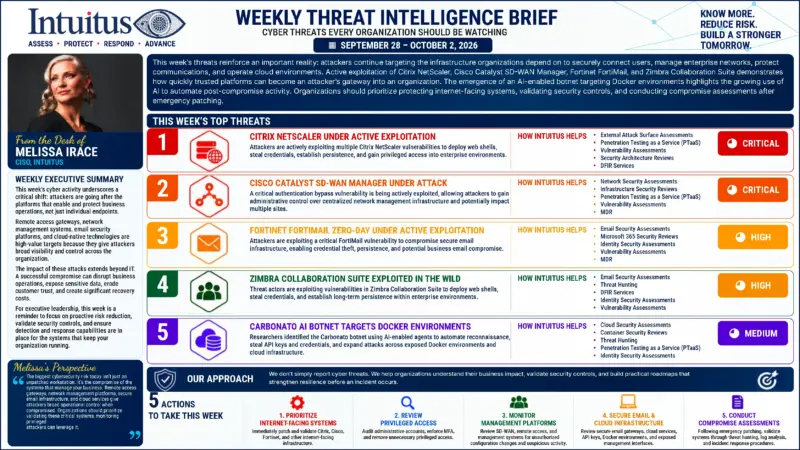
Weekly Threat Intelligence Brief, 28 September–2 October 2026
Trusted platforms are becoming gateways for attackers: Citrix NetScaler, Cisco Catalyst SD-WAN Manager, Fortinet FortiMail, Zimbra, and an AI-enabled botnet hitting Docker.
-
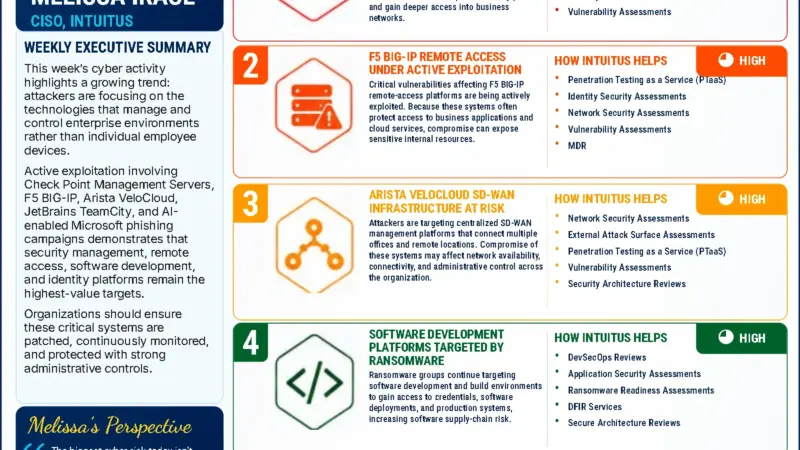
Weekly Threat Intelligence Brief, 21–25 September 2026
Attackers are going after the systems that manage security and control networks: Check Point management servers, F5 BIG-IP, Arista VeloCloud, build environments and AI-enhanced Microsoft phishing.
-
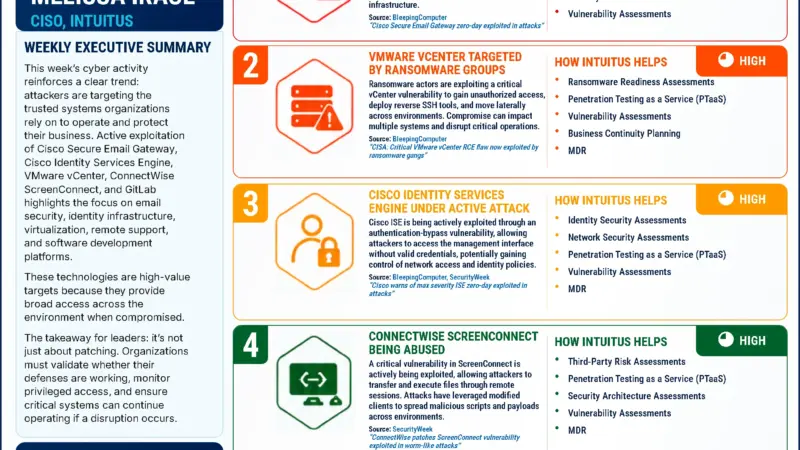
Weekly Threat Intelligence Brief, 14–18 September 2026
Attackers are going after trusted management and security platforms: Cisco Secure Email Gateway, VMware vCenter, Cisco ISE, ConnectWise ScreenConnect and GitLab.
-
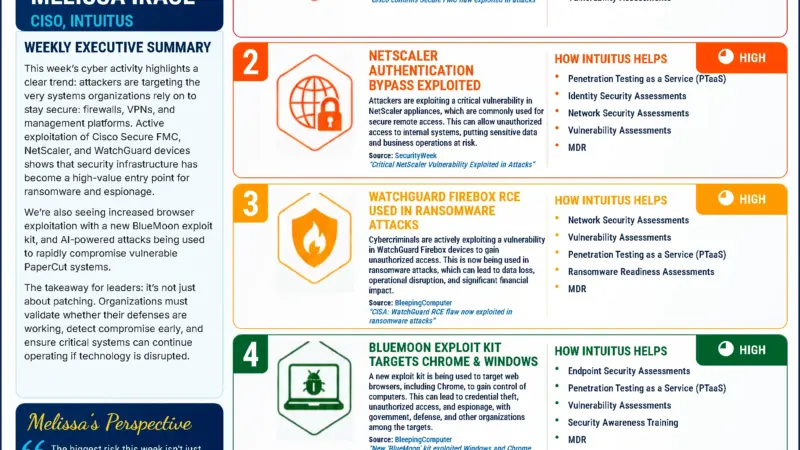
Weekly Threat Intelligence Brief, 7–11 September 2026
Attackers are going after the systems that keep organizations secure: Cisco Secure FMC, NetScaler and WatchGuard devices, plus the new BlueMoon exploit kit and an AI-driven PaperCut campaign.
-
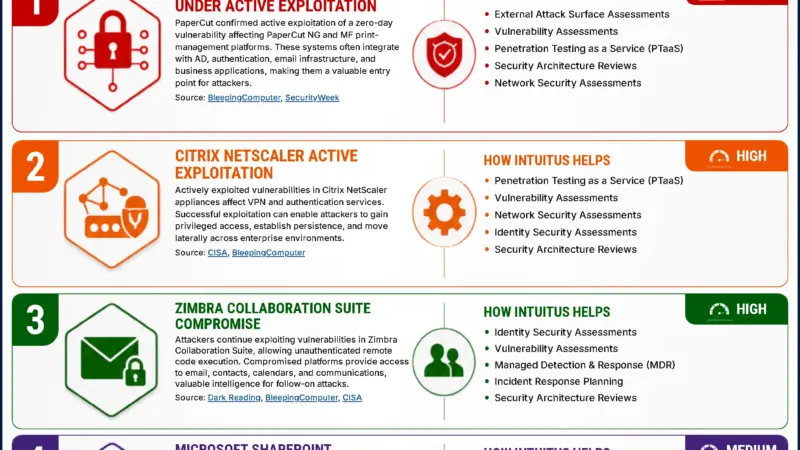
Weekly Threat Intelligence Brief, 24–28 August 2026
Five threats worth watching this week: a PaperCut zero-day under active exploitation, Citrix NetScaler, Zimbra, a SharePoint RCE chain, and pressure on critical infrastructure and supply chains.
-
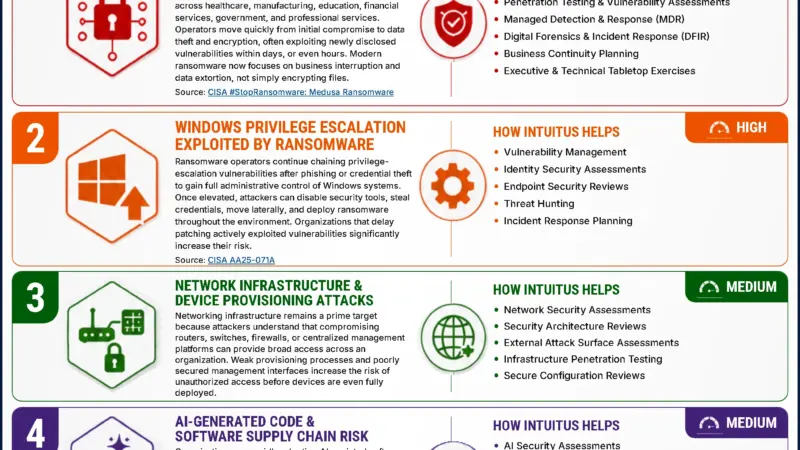
Weekly Threat Intelligence Brief, 17–21 August 2026
Five threats worth watching this week: Medusa ransomware, Windows privilege escalation, attacks on network infrastructure, risk in AI-generated code, and pressure on critical infrastructure and OT.
Start the conversation
Talk to a cybersecurity engineer — not a sales rep.
Tell us your industry and where you are today. We’ll route you to the right specialist and a practical next step — no pressure, no jargon.