
From the Desk of Melissa Irace, CISO
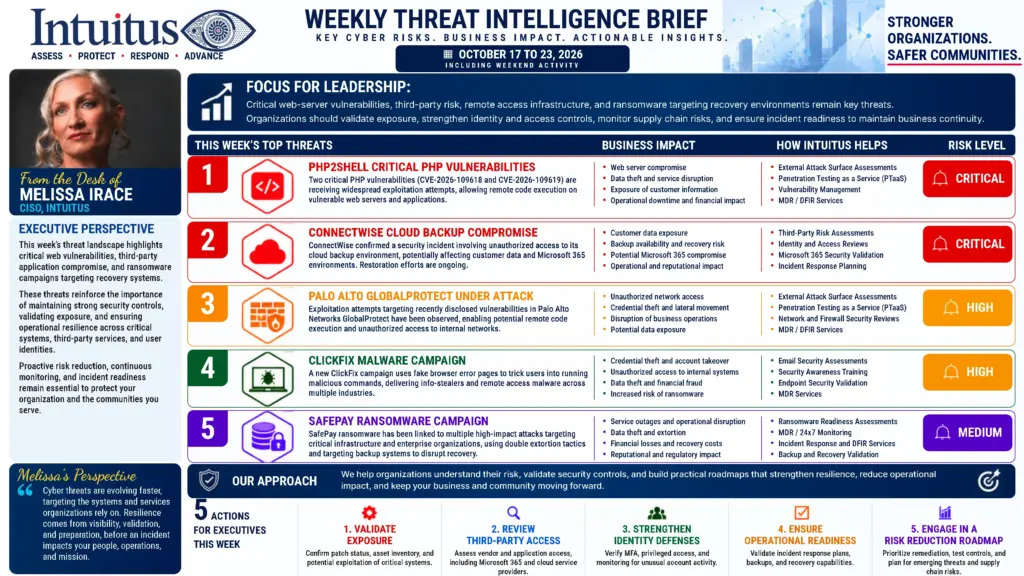
Critical web-server vulnerabilities, third-party risk, remote access infrastructure, and ransomware targeting recovery environments remain key threats. Organizations should validate exposure, strengthen identity and access controls, monitor supply chain risks, and ensure incident readiness to maintain business continuity.
Executive perspective
This week’s threat landscape highlights critical web vulnerabilities, third-party application compromise, and ransomware campaigns targeting recovery systems.
These threats reinforce the importance of maintaining strong security controls, validating exposure, and ensuring operational resilience across critical systems, third-party services, and user identities.
Proactive risk reduction, continuous monitoring, and incident readiness remain essential to protect your organization and the communities you serve.
Melissa’s perspective
“Cyber threats are evolving faster, targeting the systems and services organizations rely on. Resilience comes from visibility, validation, and preparation, before an incident impacts your people, operations, and mission.”
This week’s top threats
01 · Critical
PHP2Shell: critical PHP vulnerabilities
Two critical PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619) are receiving widespread exploitation attempts, allowing remote code execution on vulnerable web servers and applications.
How Intuitus helps
- External Attack Surface Assessments
- Penetration Testing as a Service (PTaaS)
- Vulnerability Management
- MDR and DFIR Services
02 · Critical
ConnectWise cloud backup compromise
ConnectWise confirmed a security incident involving unauthorized access to its cloud backup environment, potentially affecting customer data and Microsoft 365 environments. Restoration efforts are ongoing.
How Intuitus helps
- Third-Party Risk Assessments
- Identity and Access Reviews
- Microsoft 365 Security Validation
- Incident Response Planning
03 · High
Palo Alto GlobalProtect under attack
Exploitation attempts targeting recently disclosed vulnerabilities in Palo Alto Networks GlobalProtect have been observed, enabling potential remote code execution and unauthorized access to internal networks.
How Intuitus helps
- External Attack Surface Assessments
- Penetration Testing as a Service (PTaaS)
- Network and Firewall Security Reviews
- MDR and DFIR Services
04 · High
ClickFix malware campaign
A new ClickFix campaign uses fake browser error pages to trick users into running malicious commands, delivering info-stealers and remote access malware across multiple industries.
How Intuitus helps
- Email Security Assessments
- Security Awareness Training
- Endpoint Security Validation
- MDR Services
05 · Medium
SafePay ransomware campaign
SafePay ransomware has been linked to multiple high-impact attacks targeting critical infrastructure and enterprise organizations, using double extortion tactics and targeting backup systems to disrupt recovery.
How Intuitus helps
- Ransomware Readiness Assessments
- MDR and 24/7 Monitoring
- Incident Response and DFIR Services
- Backup and Recovery Validation
Our approach
We help organizations understand their risk, validate security controls, and build practical roadmaps that strengthen resilience, reduce operational impact, and keep your business and community moving forward.
Five actions for executives this week
- Validate exposure. Confirm patch status, asset inventory, and potential exploitation of critical systems.
- Review third-party access. Assess vendor and application access, including Microsoft 365 and cloud service providers.
- Strengthen identity defenses. Verify MFA, privileged access, and monitoring for unusual account activity.
- Ensure operational readiness. Validate incident response plans, backups, and recovery capabilities.
- Engage in a risk reduction roadmap. Prioritize remediation, test controls, and plan for emerging threats and supply chain risks.