
A suspension or revision of a CMMC implementation milestone does not automatically eliminate existing contractual cybersecurity obligations, including applicable DFARS requirements and the protection of covered defense information.
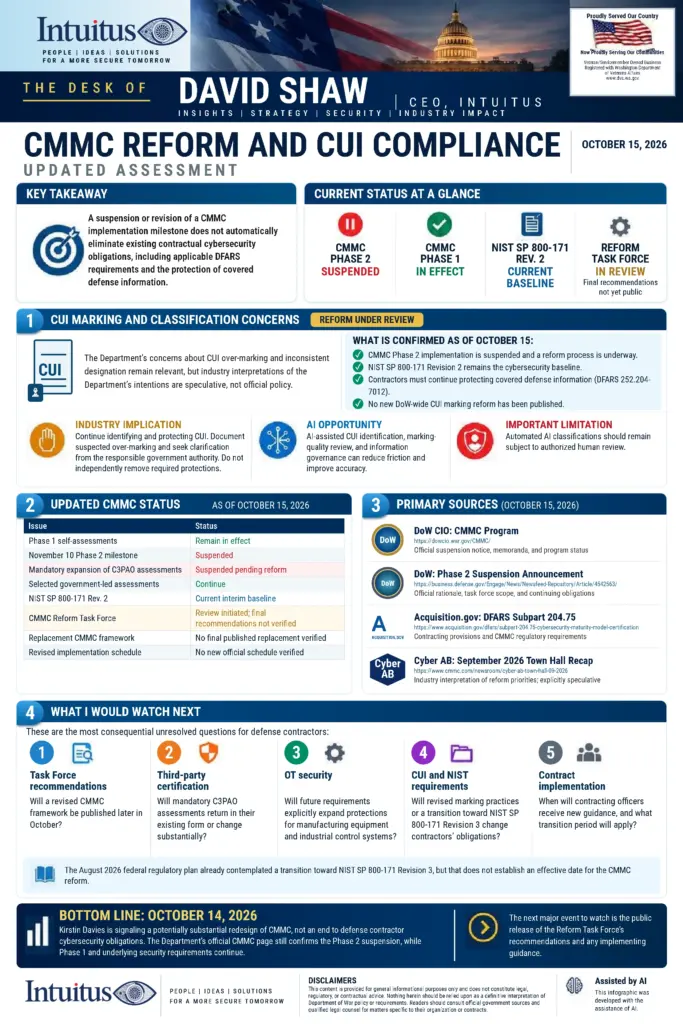
Current status at a glance
- CMMC Phase 2: suspended.
- CMMC Phase 1: in effect.
- NIST SP 800-171 Rev. 2: the current baseline.
- Reform Task Force: in review. Final recommendations are not yet public.
CUI marking and classification concerns
The Department’s concerns about CUI over-marking and inconsistent designation remain relevant, but industry interpretations of the Department’s intentions are speculative, not official policy. Reform is under review.
What is confirmed as of 15 October:
- CMMC Phase 2 implementation is suspended and a reform process is underway.
- NIST SP 800-171 Revision 2 remains the cybersecurity baseline.
- Contractors must continue protecting covered defense information (DFARS 252.204-7012).
- No new DoW-wide CUI marking reform has been published.
- Industry implication. Continue identifying and protecting CUI. Document suspected over-marking and seek clarification from the responsible government authority. Do not independently remove required protections.
- AI opportunity. AI-assisted CUI identification, marking-quality review, and information governance can reduce friction and improve accuracy.
- Important limitation. Automated AI classifications should remain subject to authorized human review.
Updated CMMC status, as of 15 October 2026
- Phase 1 self-assessments: remain in effect.
- 10 November Phase 2 milestone: suspended.
- Mandatory expansion of C3PAO assessments: suspended pending reform.
- Selected government-led assessments: continue.
- NIST SP 800-171 Rev. 2: current interim baseline.
- CMMC Reform Task Force: review initiated; final recommendations not verified.
- Replacement CMMC framework: no final published replacement verified.
- Revised implementation schedule: no new official schedule verified.
What I would watch next
These are the most consequential unresolved questions for defense contractors:
- Task Force recommendations. Will a revised CMMC framework be published later in October?
- Third-party certification. Will mandatory C3PAO assessments return in their existing form or change substantially?
- OT security. Will future requirements explicitly expand protections for manufacturing equipment and industrial control systems?
- CUI and NIST requirements. Will revised marking practices or a transition toward NIST SP 800-171 Revision 3 change contractors’ obligations?
- Contract implementation. When will contracting officers receive new guidance, and what transition period will apply?
The August 2026 federal regulatory plan already contemplated a transition toward NIST SP 800-171 Revision 3, but that does not establish an effective date for the CMMC reform.
Bottom line
Kirsten Davies is signaling a potentially substantial redesign of CMMC, not an end to defense contractor cybersecurity obligations. The Department’s official CMMC page still confirms the Phase 2 suspension, while Phase 1 and underlying security requirements continue.
The next major event to watch is the public release of the Reform Task Force’s recommendations and any implementing guidance.
Primary sources, 15 October 2026: DoW CIO CMMC Program page (official suspension notice, memoranda and program status); DoW Phase 2 suspension announcement (official rationale, task force scope and continuing obligations); Acquisition.gov DFARS Subpart 204.75 (contracting provisions and CMMC regulatory requirements); Cyber AB September 2026 Town Hall recap (industry interpretation of reform priorities, explicitly speculative). This content is provided for general informational purposes only and does not constitute legal, regulatory, or contractual advice. Readers should consult official government sources and qualified legal counsel for matters specific to their organization or contracts.