
Phase II is paused. Cyber obligations are not. CMMC has not been cancelled: Phase I remains in force while the Department of War reviews the certification model. This open-source assessment reflects what was publicly known as of 1 October 2026.
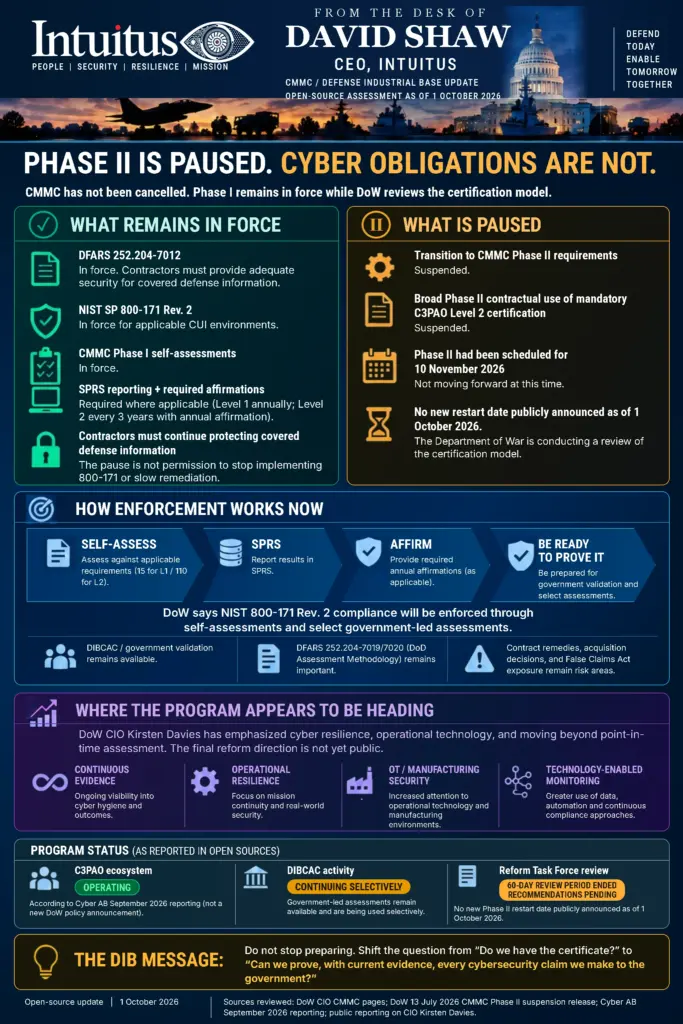
What remains in force
- DFARS 252.204-7012. In force. Contractors must provide adequate security for covered defense information.
- NIST SP 800-171 Rev. 2. In force for applicable CUI environments.
- CMMC Phase I self-assessments. In force.
- SPRS reporting and required affirmations. Required where applicable: Level 1 annually, Level 2 every three years with annual affirmation.
- Protecting covered defense information. Contractors must continue. The pause is not permission to stop implementing 800-171 or to slow remediation.
What is paused
- Transition to CMMC Phase II requirements. Suspended.
- Broad Phase II contractual use of mandatory C3PAO Level 2 certification. Suspended.
- Phase II had been scheduled for 10 November 2026. Not moving forward at this time.
- No new restart date publicly announced as of 1 October 2026. The Department of War is conducting a review of the certification model.
How enforcement works now
DoW says NIST 800-171 Rev. 2 compliance will be enforced through self-assessments and select government-led assessments. In practice, that means four steps:
- Self-assess against applicable requirements (15 for Level 1, 110 for Level 2).
- Report results in SPRS.
- Affirm. Provide required annual affirmations, as applicable.
- Be ready to prove it. Be prepared for government validation and select assessments.
DIBCAC and government validation remain available. DFARS 252.204-7019 and 7020 (the DoD Assessment Methodology) remain important. Contract remedies, acquisition decisions, and False Claims Act exposure remain risk areas.
Where the program appears to be heading
DoW CIO Kirsten Davies has emphasized cyber resilience, operational technology, and moving beyond point-in-time assessment. The final reform direction is not yet public. Four themes stand out:
- Continuous evidence. Ongoing visibility into cyber hygiene and outcomes.
- Operational resilience. Focus on mission continuity and real-world security.
- OT and manufacturing security. Increased attention to operational technology and manufacturing environments.
- Technology-enabled monitoring. Greater use of data, automation and continuous compliance approaches.
Program status, as reported in open sources
- C3PAO ecosystem: operating. According to Cyber AB September 2026 reporting (not a new DoW policy announcement).
- DIBCAC activity: continuing selectively. Government-led assessments remain available and are being used selectively.
- Reform Task Force review: 60-day review period ended, recommendations pending. No new Phase II restart date publicly announced as of 1 October 2026.
The DIB message
Do not stop preparing. Shift the question from “Do we have the certificate?” to “Can we prove, with current evidence, every cybersecurity claim we make to the government?”
Open-source update, 1 October 2026. Sources reviewed: DoW CIO CMMC pages; DoW 13 July 2026 CMMC Phase II suspension release; Cyber AB September 2026 reporting; public reporting on CIO Kirsten Davies.